There was unauthorized outside access to the membership system of Hollys, a Korean coffee chain, and personal data of members who joined before February 11, 2020 was leaked It included IDs and passwords, addresses, and even Duplicate Registration Information (DI)
The operator, KG F&B, confirmed the leak on October 16 and has not yet disclosed how many members were affected
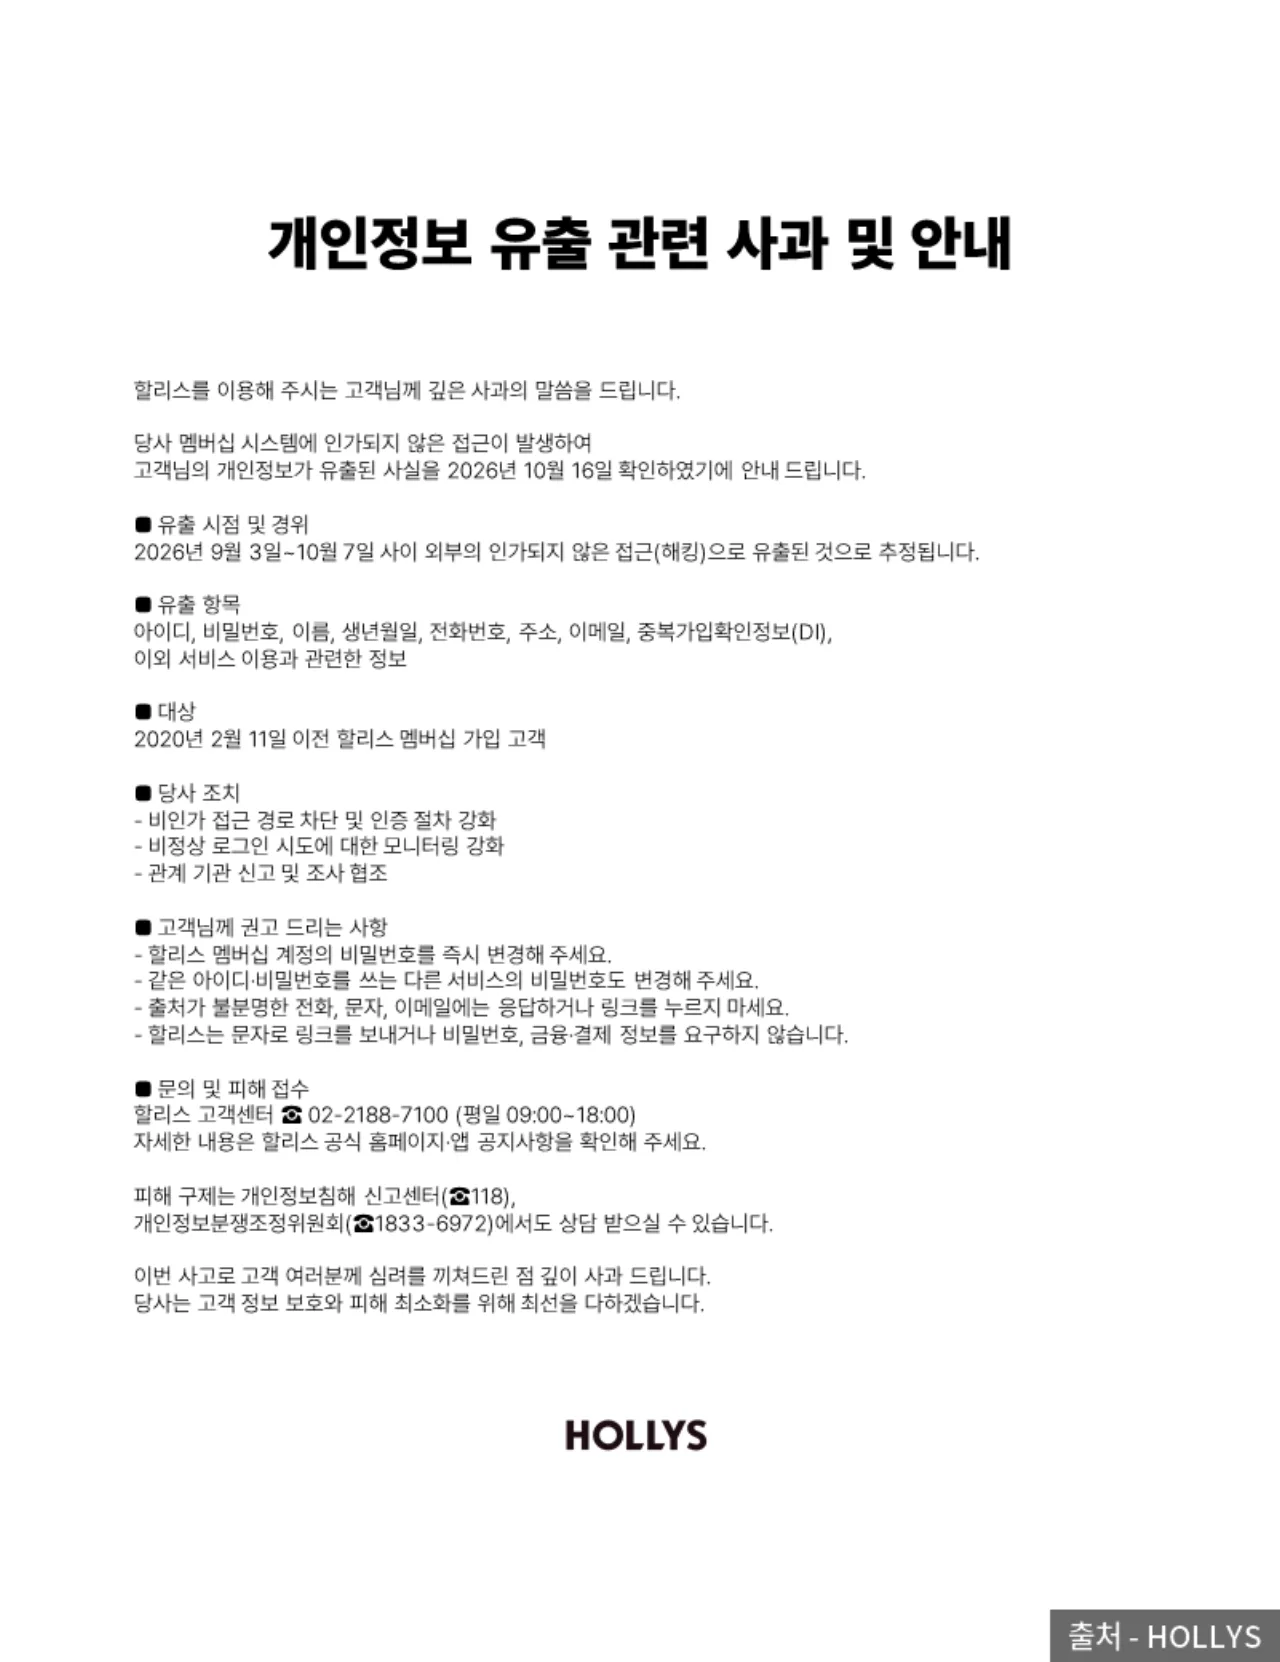 Hollys apology and notice about the personal data leak — Source: HOLLYS
Timeline
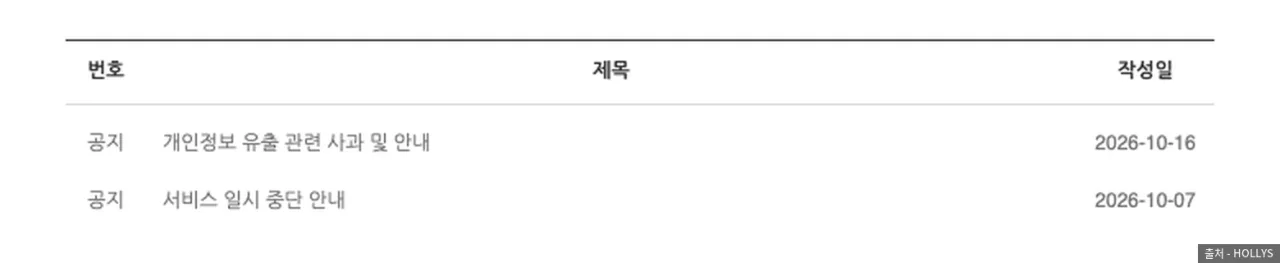 Hollys notice list showing the October 16 apology and the October 7 service suspension notice — Source: HOLLYS
According to the Hollys notice, the leak is estimated to have occurred over 35 days, from September 3 to October 7, 2026 The company confirmed the leak on October 16 and posted an apology on its website at 9:36 p.m. the same day
Text messages to members were sent on October 18 That means the unauthorized access that went on for 35 days was not detected during that period
| Date | Event |
|---|---|
| September 3 | Unauthorized access begins (estimated) |
| October 7 | Unauthorized access ends (estimated) |
| October 7 | Notice of October 19 server migration |
| October 16 | Leak confirmed, apology posted |
| October 18 | Text messages sent to members |
The October 7 notice announced that website and app services would be suspended early on October 19 for a server migration The company has not said how this work relates to the leak
Article 39 of the Enforcement Decree of the Personal Information Protection Act requires notifying data subjects within 72 hours of learning of a leak The same-day notice and the text two days later are within that deadline
What was leaked and what isn’t confirmed
The leaked items listed in the notice are account information, contact details, addresses, DI, and service usage information Those affected were limited to Hollys membership customers who joined before February 11, 2020
| Item | What the notice says |
|---|---|
| ID, password | Leaked |
| Name, date of birth, phone | Leaked |
| Address, email | Leaked |
| DI (Duplicate Registration Information) | Leaked |
| Number of affected members | Not disclosed |
| How passwords were stored | Not disclosed |
| Payment card information | Not in the notice |
Under the Hollys privacy policy, card payments are processed by payment gateways such as KG Inicis Card numbers are not among the items in the notice
The company also hasn’t explained why the cutoff date of February 11, 2020 was set It only stated that members who joined after that are not affected; the reason is unconfirmed
How risky the passwords and DI are
 Concept shot of the risk of one password opening accounts on several services — Source: concept shot · self-generated with agy
Korea’s standards for measures to secure personal data require passwords to be stored with one-way encryption so they can’t be decrypted The Hollys privacy policy also says passwords are protected by encryption, but how the leaked data was stored has not been disclosed
🔑 Passwords
Even with one-way encryption, short or common passwords can be guessed and confirmed through brute-force attacks If you use the same ID and password on other services, the risk of account takeover grows
Hollys accounts are linked to the balance of the rechargeable Hollys Card and Crown rewards If you leave your password as is, the account could be taken over and the balance spent on payments!!
It’s an attack that tries leaked IDs and passwords to log in to other sites This is called credential stuffing
That’s why Hollys also advised changing passwords for other services that use the same ID and password
🪪 DI (Duplicate Registration Information)
DI is a value generated by an identity verification agency to stop the same person from signing up twice on one site
DI has a different value for each site, so it’s hard to link with data from other services That’s how it differs from CI (Connecting Information), which uses the same value across all services
Still, since it leaked along with names, dates of birth, phone numbers, and addresses, it could be abused for texts and calls impersonating you I explained the difference between CI and DI in detail in part 2 of the TVING leak series
🔗 Link - https://blog.naver.com/rottensweetpotato/224314384302
Why members from before 2020 are affected
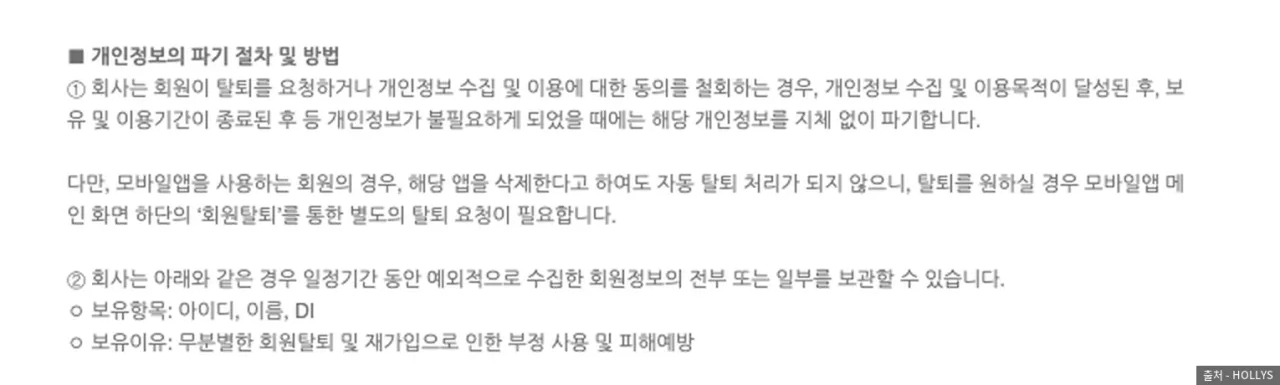 Destruction procedure clause in the Hollys privacy policy, noting that deleting the app is not account deletion — Source: HOLLYS
All of those affected are people whose member data had remained for more than six years The Hollys privacy policy states that data is destroyed when you delete your account or the purpose is achieved
The same clause separately says deleting the app does not automatically delete your account
There used to be a validity period rule that required separating or destroying data from accounts unused for a year A 2023 amendment removed this obligation, so even long-unused accounts can be kept until they are deleted
Even after account deletion, Hollys keeps ID, name, and DI for 30 days to prevent re-registration abuse
What to do now
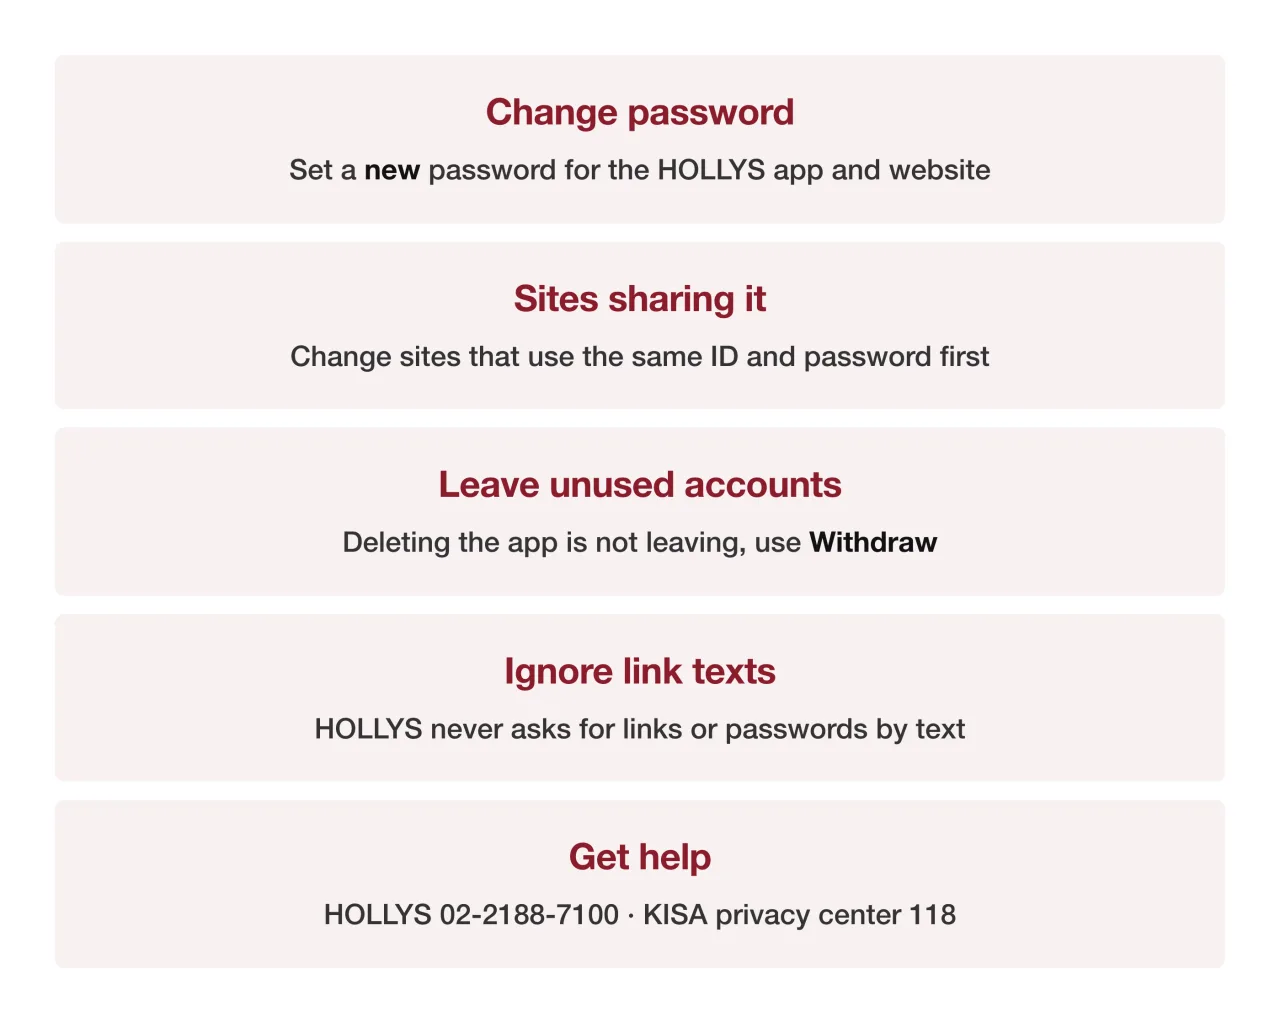 Five steps people affected by the Hollys leak should take now — Source: self-rendered based on the Hollys notice
You can check whether you’re affected with the Hollys customer center (02-2188-7100, weekdays 9 a.m.–6 p.m.) There is no individual lookup screen, so if you joined before February 2020, it’s safer to change your password first
The Personal Information Infringement Report Center (118) and the Personal Information Dispute Mediation Committee (1833-6972) take consultations on remedies
🔗 Link - https://privacy.kisa.or.kr
The three things the operator needs to disclose are the number of affected members, how passwords were stored, and the intrusion route Affected people can judge their risk only once the scale of damage and the password storage method are disclosed
Sources
- [HOLLYS] Apology and notice about the personal data leak (2026-10-16, notice image in this post)
- [HOLLYS] Temporary service suspension notice (2026-10-07, October 19 server migration)
- [HOLLYS] Privacy policy (destruction procedure, items kept after account deletion, payment outsourcing)
- [Boan News] Customer personal data leaked in Hollys hack (2026-10-18)
- [IT Daily] Hollys membership customer personal data leaked (2026-10-18)
- [Korea Law Information Center] Enforcement Decree of the Personal Information Protection Act Article 39 (leak notification), standards for measures to secure personal data